
CrowdStrike and federal authorities dismantle Russian malware that secretly stole crypto for 8 years
 2 weeks ago
9355
Related
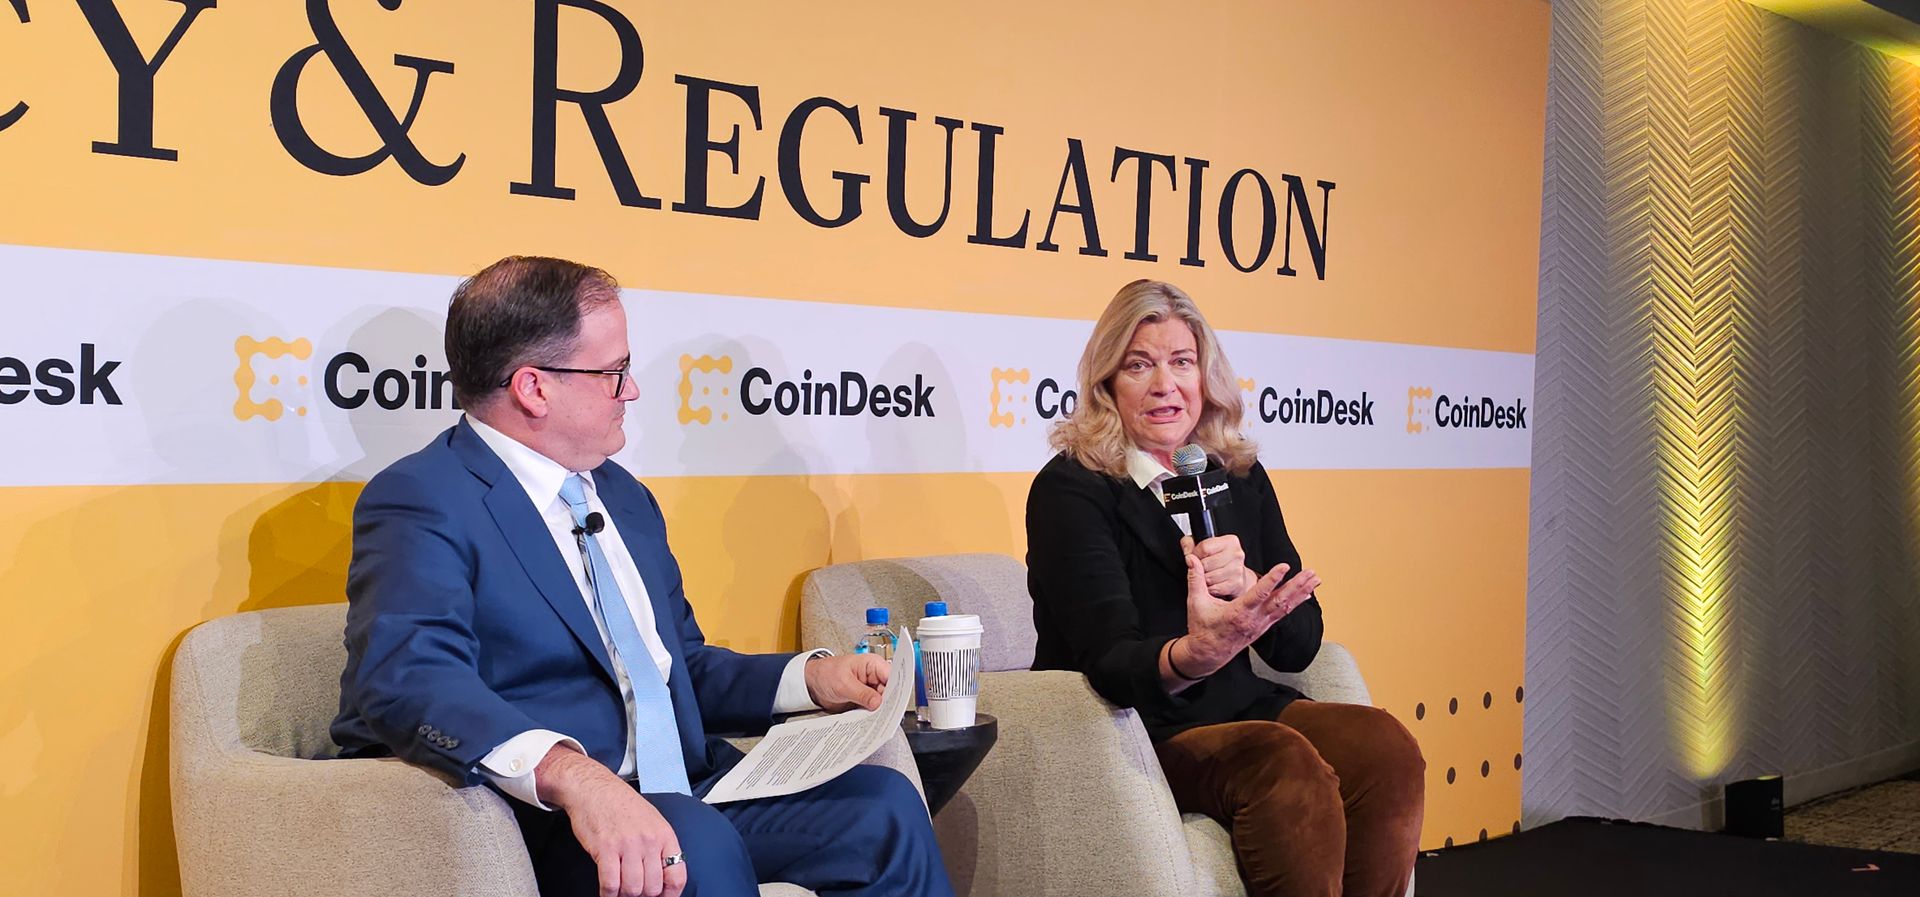
Democrats 'chose visceral hatred for' Donald Trump over cryp...
8 minutes ago
175

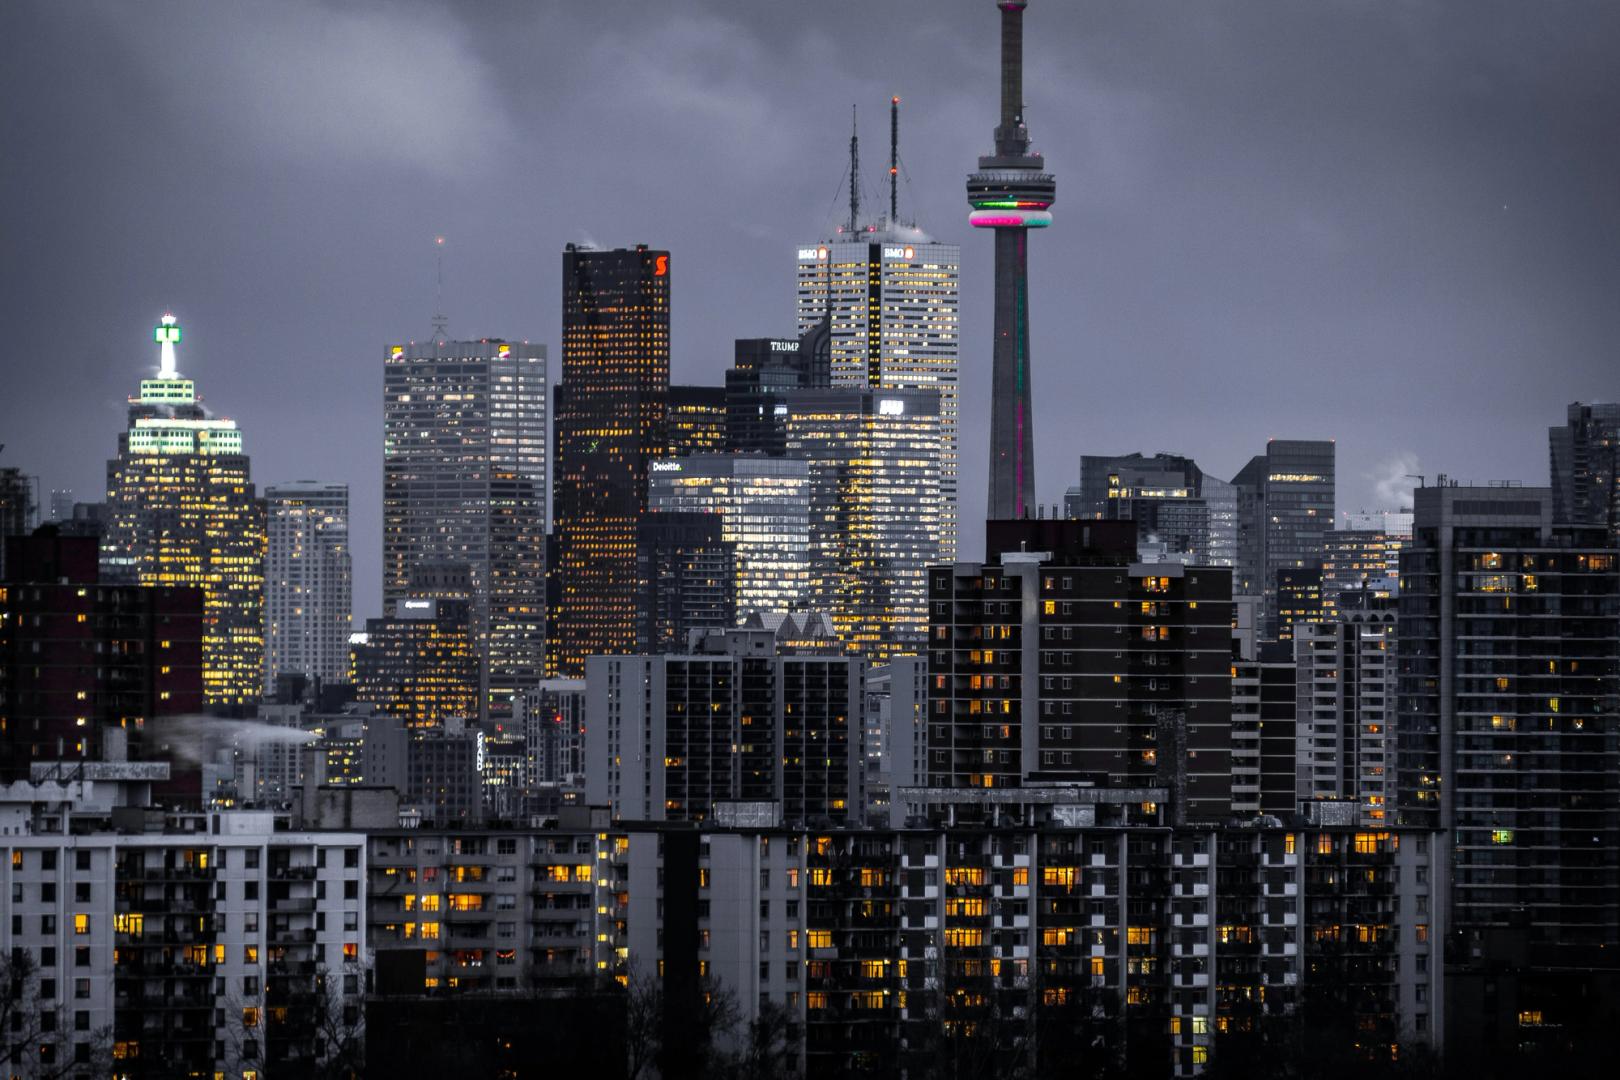
Canada's 'Big Six' banks to launch interbank tokenized depos...
4 hours ago
599
Next for the U.S. SEC: Agency's chief crypto counsel illumin...
6 hours ago
923

Machine learning algorithm sets Zcash (ZEC) price for Octobe...
6 hours ago
970

European central banks push to expand stablecoin yield ban t...
7 hours ago
1121
Popular
Bitcoin loses touch with the Dollar Index, U.S. stocks ahead...
6 days ago
10459
Two Prime makes onchain finance push with $10 million-backed...
6 days ago
9519
Bessent to raise AI, rare earths with China's He as tech riv...
3 days ago
9145
Italy investigates government email breach linked to Revolut...
6 days ago
8934
Zcash holders back 25-second blocks, vote to keep ZEC halvin...
6 days ago
8708
OpenAI discloses 6 new cases of ‘misaligned’ AI behavior
5 days ago
8325
OpenAI’s $280B compute build-out is repricing Bitcoin miners...
3 days ago
7911
Circle debuts Arc blockchain which Jeremy Allaire calls ‘mor...
6 days ago
7716
Goldman Sachs Expects Another Fed Rate Hike in October
5 days ago
7672
OpenAI discloses 6 new cases of ‘misaligned’ AI behavior
5 days ago
7633
Payward plans to offer U.S. clients onchain perpetual future...
6 days ago
7571
ECB President Christine Lagarde intervened to block Binance’...
4 days ago
7473
 English (US)
Litepaper ·
About Us ·
How It Works ·
Documentation ·
Advertise With Us ·
Privacy Policy ·
Terms & Conditions ·
Return & Refund Policy ·
Contact Us ·
Report / DMCA ·
© Cryptews 2026. All rights are reserved