 54 minutes ago
545

Alex Thorn, head of research at Galaxy Digital, says the second wave of attacks in the Coldcard wallet exploit was about 40% whitehat activity.
Thorn tracked 52.37 BTC being dispatched to an address tagged for a new recovery trust.
52.37 BTC landed in a fresh address in block 967,948
The 52.37 BTC came from coins from Wave 2 and three attacker clusters that Galaxy called Footprint AA, AU and AX, according to Thorn. Funds reached a new address confirmed in block 967,948.
The transaction carried an OP_RETURN note, a short message embedded in a Bitcoin transaction. It read “claim:cryptorecoverytrust dot com.”
Thorn pegged the haul at 2.8% of tracked exploit funds. The same transaction also sent another 3.0134 BTC with no prior tracking history to the same recovery address.
Thorn said it was probably more whitehat recovered Coldcard money. He marked the link as unconfirmed.
As part of its blockchain monitoring, Galaxy Research also detected a related transfer of 40.71 BTC, worth ~$3.31 million, on September 21.
There were 11 addresses, 20 inputs and 480 outputs in that transaction, and it also contained the same recovery-trust message.
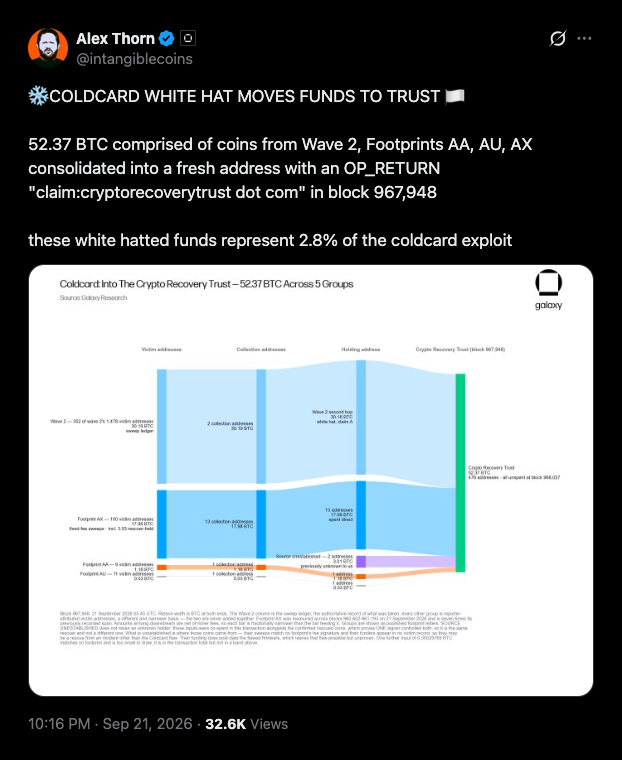 Alex Thorn’s post on X showing 52.37 BTC consolidated for the Crypto Recovery Trust.
Losses peaked near $130 million from a March 2021 firmware flaw
Whitehats are security researchers who employ attackers’ techniques to snatch exposed coins before the criminals do. Some of the outflows from victim wallets were rescues, with coins parked until owners turn up.
Victims can search wallet addresses at cryptorecoverytrust.com to see if funds were pulled to safety. Most stolen bitcoin sits dormant in attacker wallets.
The Coldcard exploit began July 30 and took place in multiple batches over the following days. Damage estimates range from over $100 million to a high of about $130 million.
Cryptopolitan’s earlier report counted ~1,816 BTC drained from over 5,200 addresses, worth between $114 million and $116 million at the time.
Some seeds generated by Coldcard firmware used a software random-number source instead of the device’s hardware generator, and attackers rebuilt those seeds offline to drain wallets.
Cryptopolitan previously traced the flaw to a firmware change in March 2021. Coinkite, maker of Coldcard, has since patched its firmware but coins already exposed under old seeds remain at risk.
The smartest crypto minds already read our newsletter. Want in? Join them.

 English (US)